Up to 1 PFLOP
FP4 AI target
Sparse-compute basis
MIRROR REALM AGENT / OWNER-CONTROLLED COMPUTE
MIRROR REALM V6 / PERSONAL AI COMMAND BOX
A portable hardware-software AI node for a private agent, encrypted personal data and distributed storage. It serves the owner first; idle compute or storage joins a collaboration network only after explicit permission.
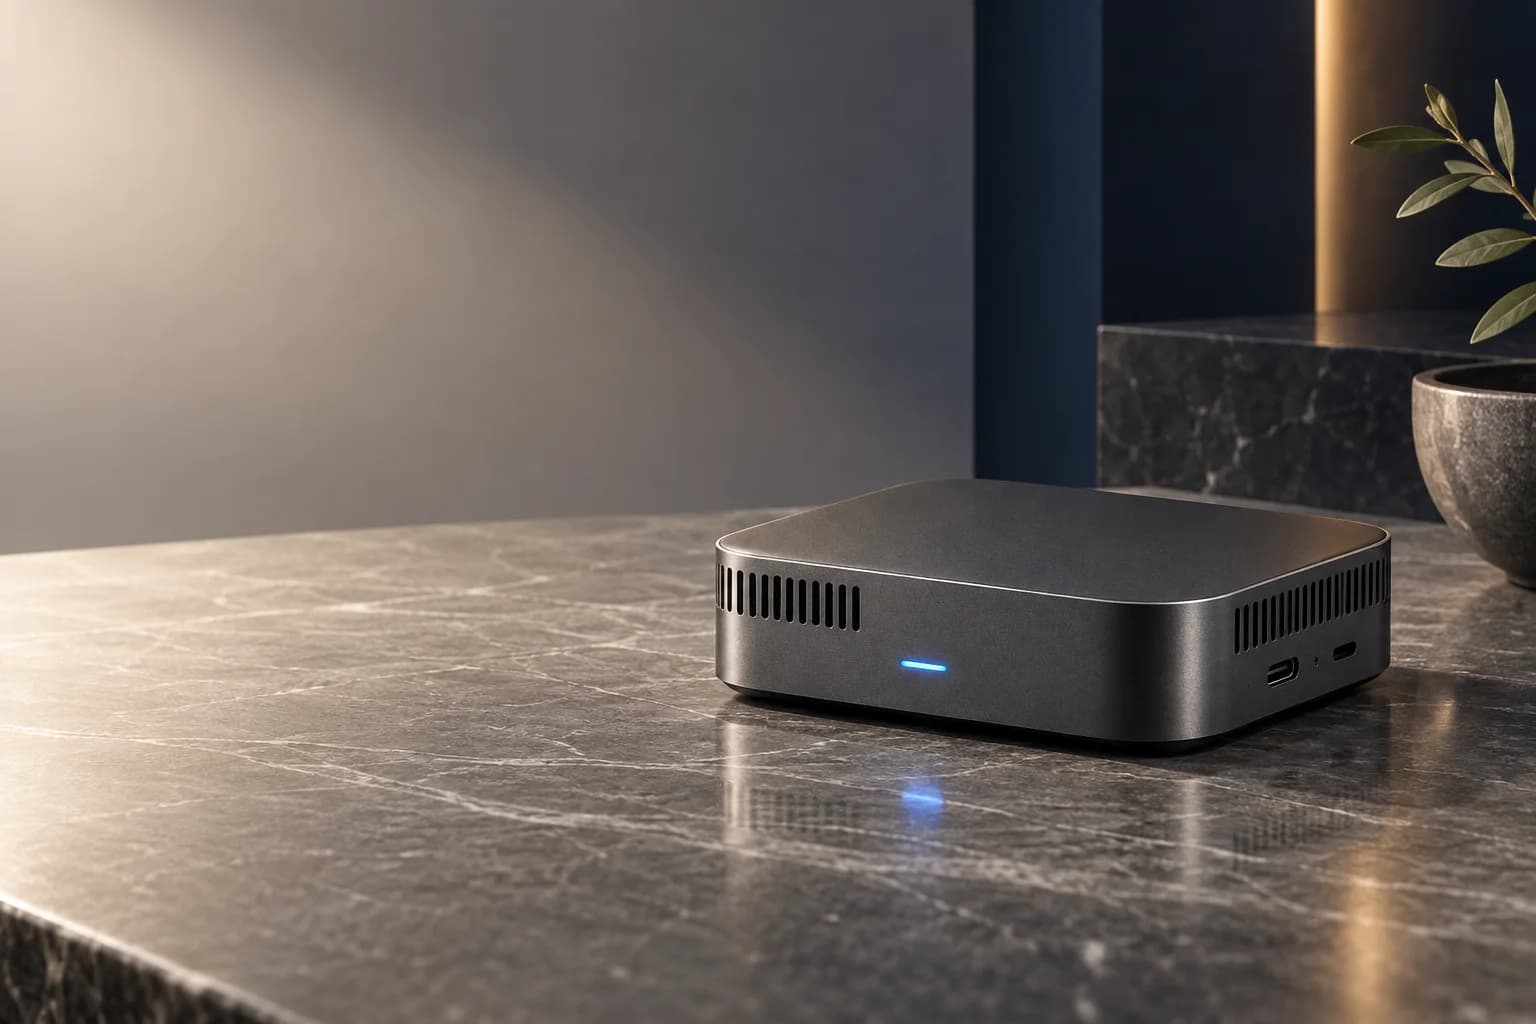
PRODUCT PROFILE / MIRROR REALM V6 / PERSONAL AI COMMAND BOX
Built for individuals, creators, developers, and small professional teams, bringing inference, knowledge, agent workflows, private data, and remote access into one desktop device.
These are reference configurations and product targets based on a GB10-class platform. They do not represent inventory, certification, or final production specifications. Prototype and workload validation are required.
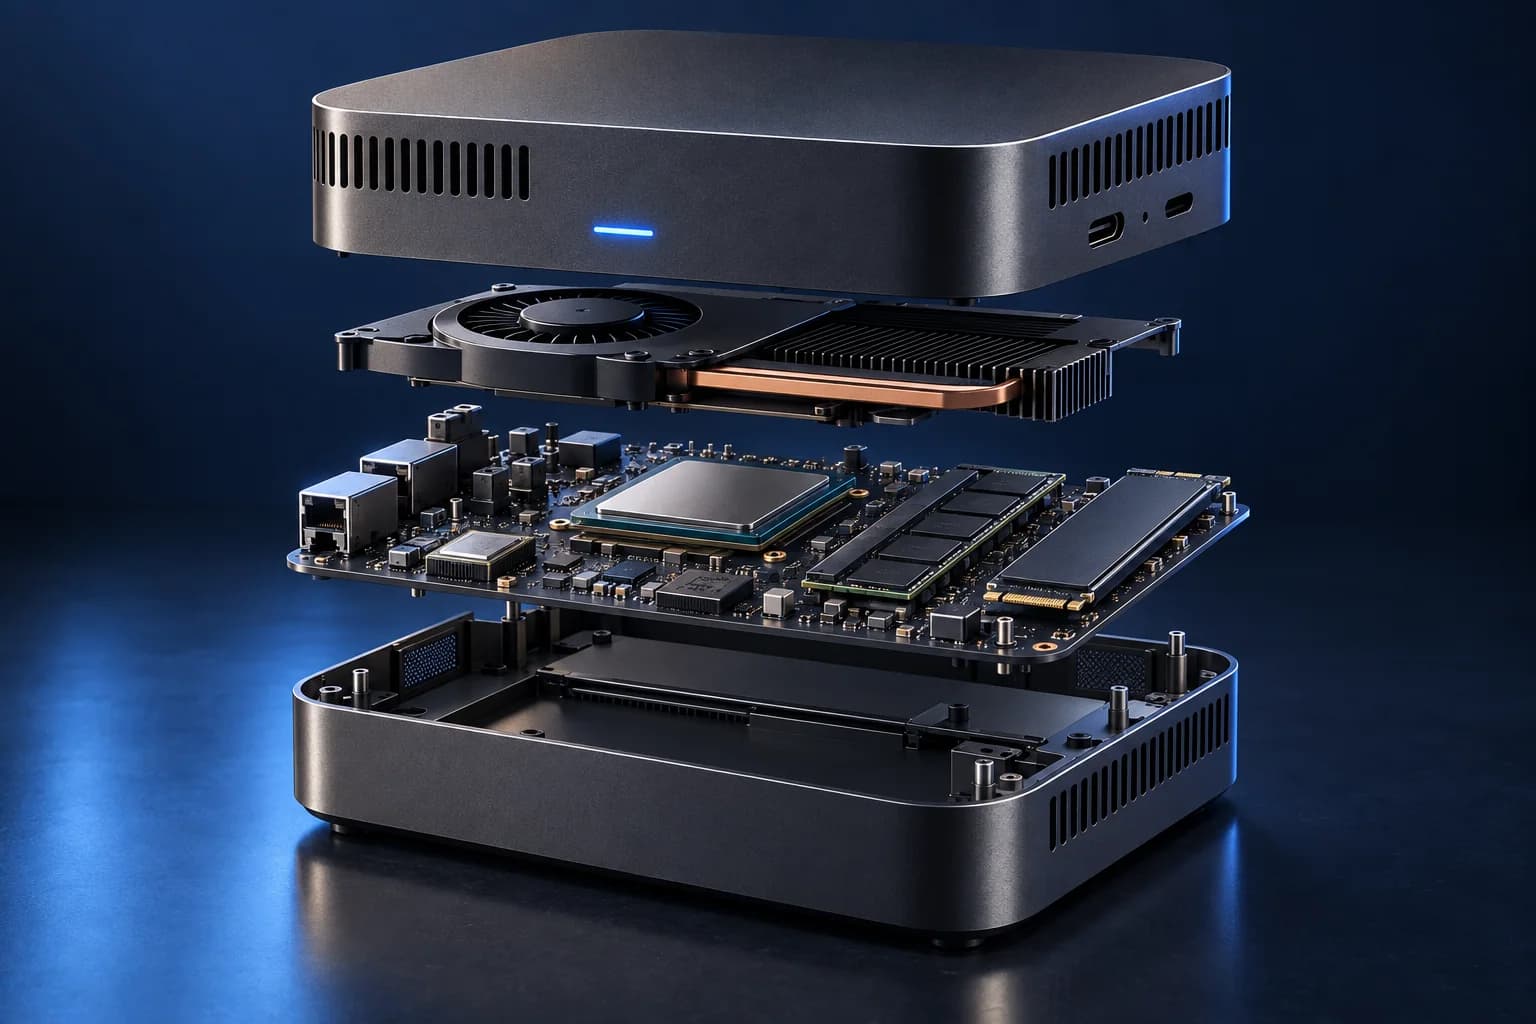
Up to 1 PFLOP
Sparse-compute basis
128GB
Local models and multimodal tasks
Up to 4TB
Models, vectors, and personal data
20-core Arm
AI orchestration and general compute
200B / 405B
Up to 200B on one; 405B on two
10GbE + 200GbE
Local access and dual-node link
01 / OWNER FIRST
Conversations, files, preferences, knowledge and agent memory remain under owner control. The device works independently and connects to approved backup or collaboration services only when permitted.
LOCAL
Local models, knowledge and long-term memory run on your device first rather than defaulting to a public cloud.
PORTABLE
Built for desk, travel and home use, carrying the owner's identity and agent environment between locations.
OWNER CONTROL
Compute, storage, sync and third-party tasks are authorized separately. Sharing is off by default and revocable.
02 / PRIVATE STACK
Each layer has an independent boundary. Cloud services handle only owner-approved backup, recovery and collaboration tasks.
Secure boot, device keys, encrypted storage and hardware identity establish a local root of trust.
Device identity is not the same as user identity
Files, media, preferences and agent memory are separated by space and processed locally first.
The owner controls classification, retention and export
Conversation, retrieval, automation and multimodal tasks run locally; approved external models are optional.
Capability depends on validated hardware and model versions
Backup, metering and Seagull Base connectivity pass through permission, isolation and audit controls.
Platform access depends on released APIs and compliance review
WORKLOADS / LOCAL FIRST
Prototyping, fine-tuning, local inference, data science, and a private assistant share one environment without sending personal data to a public cloud by default.
Validate agents, RAG, and multimodal interactions locally.
Optimize domain models with owner-controlled data.
Keep a private agent available on the device.
Analyze and experiment inside a controlled workspace.
SCALE OUT / VALIDATED TOPOLOGY
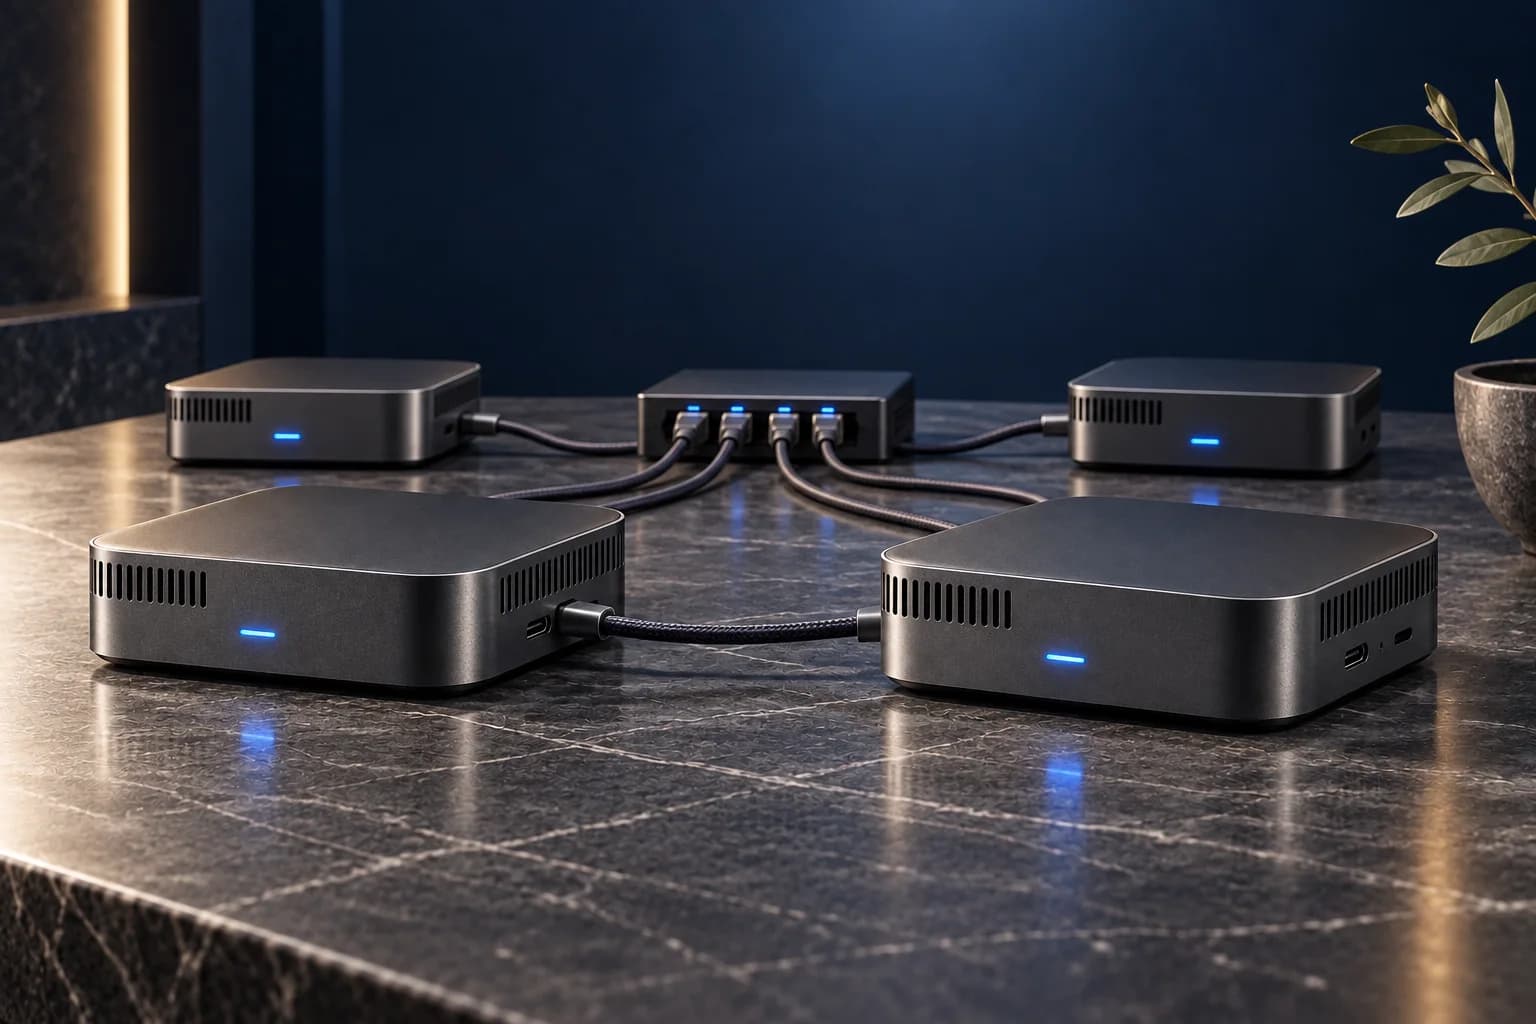
Two systems can interconnect for larger models. Three or four require a validated network topology and distributed software. Adding nodes does not automatically create one shared memory pool.
Private agent, local inference, and knowledge
High-speed link for up-to-405B model scenarios
Theoretical aggregate up to 4 PFLOPS / 512GB
Four-node figures are theoretical reference-spec aggregates, not application-performance promises. Networking, cables, libraries, and model parallelism require validation.
03 / OPERATING MODES
The three modes are independent. Owners can use private mode only or define conditions for network, battery and time.
Compute, storage and data serve the owner for assistance, creation, knowledge, automation and family memory.
No outside workloads
Encrypted data uses fragmentation and redundancy for recovery across approved nodes.
Keys are not uploaded with plaintext data
Idle resources accept constrained tasks only within temperature, power and network policies.
Metered, pausable and revocable
04 / PRIVACY & RECOVERY
The goal is to prevent direct unauthorized reading and give the owner lock, revoke and recovery controls. Security requires threat modeling, penetration testing and production validation.
Verify firmware, system and runtime integrity before personal data becomes available.
Protect user data with device-bound keys and optional owner credentials for sensitive spaces.
Remote lock, certificate revocation, session expiry and recovery policies execute when connectivity returns.
External tasks cannot access personal files, memory, camera or microphone by default.
Send only data required for a task, with local redaction or feature extraction where possible.
Show which resource was used, when, by whom and whether data left the device.
05 / SEAGULL BASE
Seagull Base is a planned collaboration interface for identity, tasks, metering and settlement. Connecting a node never opens its personal data vault.
The owner selects resource type, schedule, cap and minimum reserve.
Only verified task containers or storage fragments arrive, without personal-vault access.
Record verifiable compute time, capacity, network use and completion state.
Create usage records under platform rules; pricing, tax and settlement depend on released services.
This page defines product direction and interface boundaries. It is not a claim of a live public exchange, guaranteed income or a financial product.
PERSONAL / OWNER FIRST
For individuals and families: device, private runtime, migration, recovery and resource permissions.
INFRASTRUCTURE / PROJECT DELIVERY
For governments, campuses and enterprises: national centers, regional nodes, distributed systems and custom engineering.
Share the users, scenarios, local models, capacity, connectivity and sharing rules. We will translate them into a prototype and system plan.